Zscaler Zero Trust Exchange vs VPN: How Does It Differ?
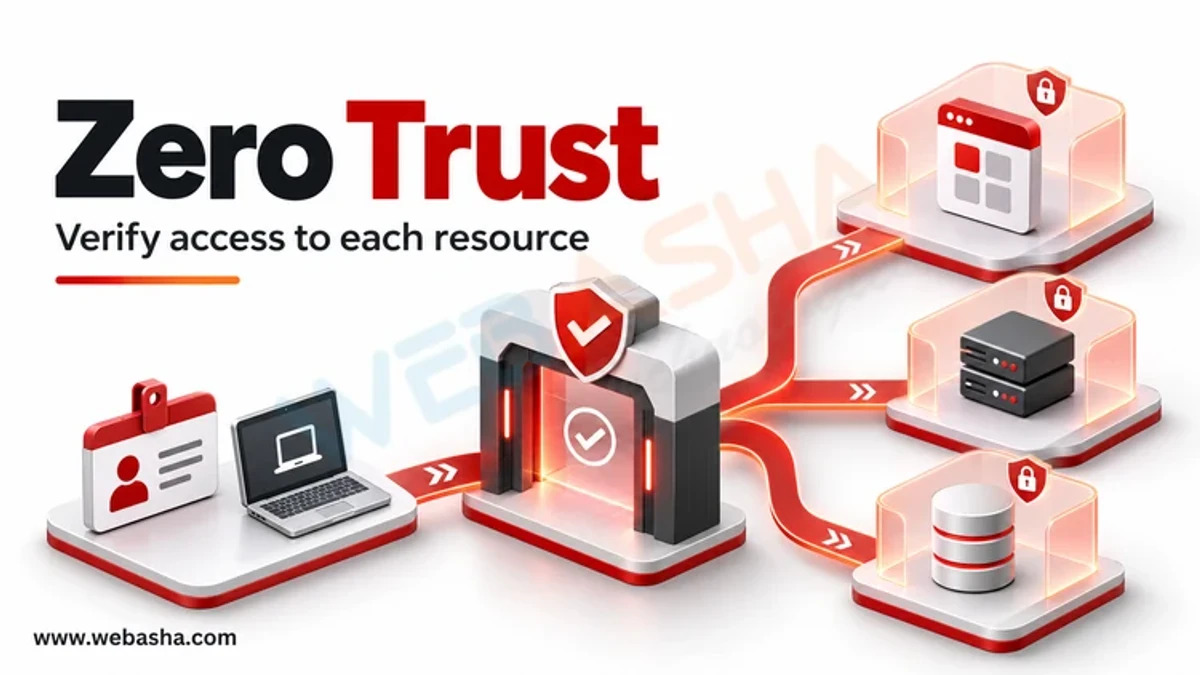
The Zscaler Zero Trust Exchange is a cloud-delivered security platform that sits between users and the applications they use. Instead of placing a remote user on the corporate network, as a traditional VPN does, it checks identity, device posture and policy for each request and then connects the user only to the specific application allowed.
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
Also covers: Network Security
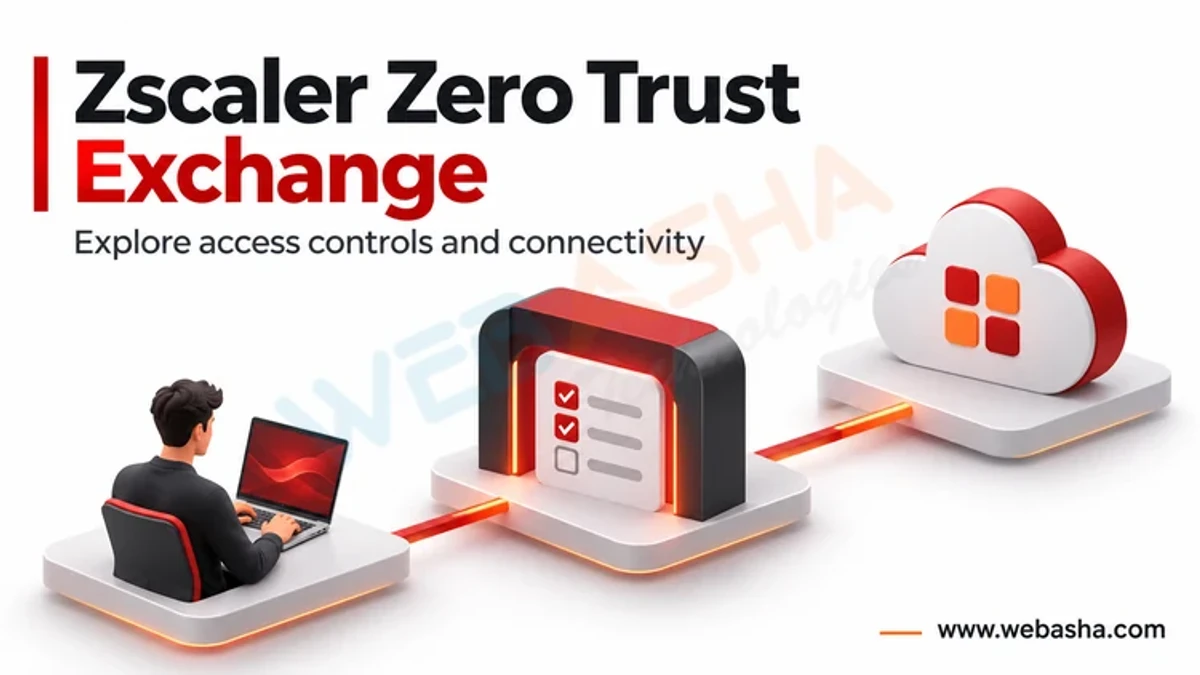
Quick answer: The Zscaler Zero Trust Exchange is a cloud-delivered security platform that sits between users and the applications they use. Instead of placing a remote user on the corporate network, as a traditional VPN does, it checks identity, device posture and policy for each request and then connects the user only to the specific application allowed. Private apps are not exposed to the internet, and users never get broad network access. This follows the zero trust model in NIST SP 800-207. A VPN encrypts the tunnel but usually trusts the user once connected, which makes lateral movement easier after a stolen login.
Key takeaways
- A VPN connects a user to a network; the Zero Trust Exchange connects a user to an application.
- Zero trust means no implicit trust based on network location (NIST SP 800-207).
- App-level brokering reduces the attack surface and lateral movement.
- Internet-facing VPN gateways are frequent targets in CISA's exploited vulnerabilities list.
- Zero trust is an architecture; any single product is only part of it.
Table of Contents
- What Does Zero Trust Mean?
- What Is the Zscaler Zero Trust Exchange?
- How Does a Traditional VPN Work?
- How Do the Two Approaches Compare?
- Why Are Organisations Moving Away From VPNs?
- How Should You Plan a Migration?
- References
What Does Zero Trust Mean?
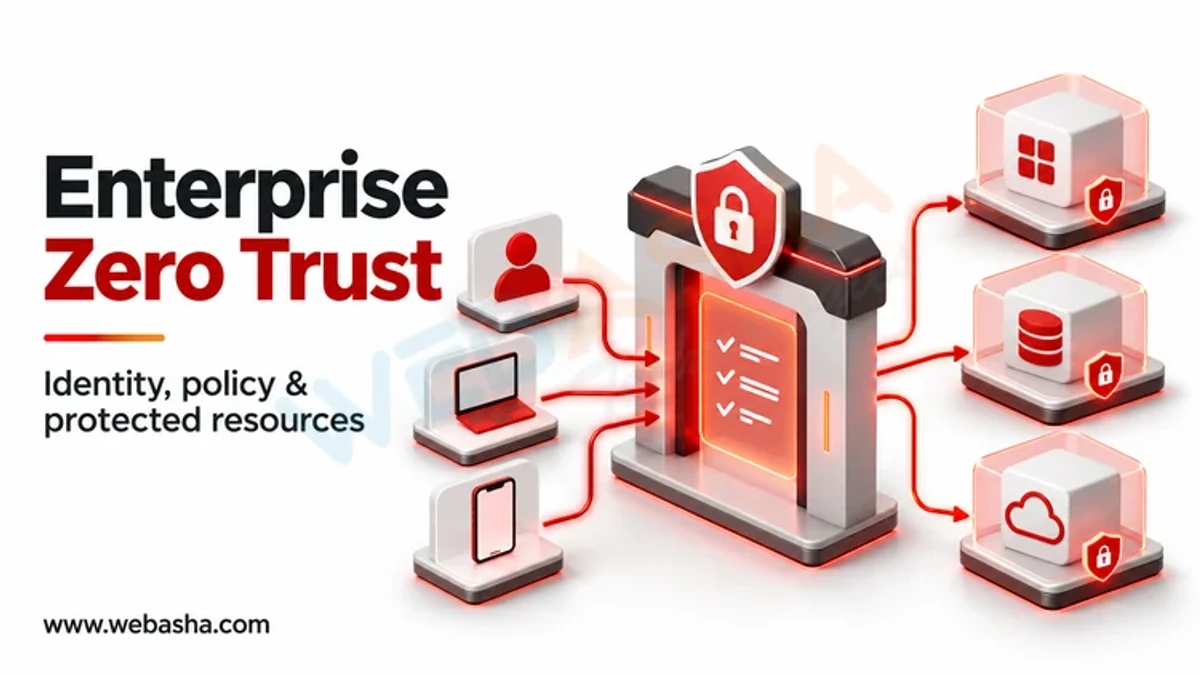
NIST SP 800-207 defines zero trust as moving defences from static network perimeters to users, assets and resources. Every access request is evaluated by a policy engine and enforced by a policy enforcement point, using identity, device state and context. CISA's Zero Trust Maturity Model breaks this into five pillars: identity, devices, networks, applications and workloads, and data. Read our sibling post on zero trust security basics.
What Is the Zscaler Zero Trust Exchange?
Zscaler describes the Zero Trust Exchange as a cloud platform that brokers connections between users, devices, workloads and applications. Two well-known services run on it:
- Zscaler Internet Access (ZIA): a secure web gateway for internet and SaaS traffic, with URL filtering, TLS inspection and data loss prevention.
- Zscaler Private Access (ZPA): access to internal apps through outbound-only connectors, so the apps have no inbound listening ports on the internet.
In NIST terms, the platform acts as the policy enforcement point, with identity providers and device signals feeding the decision.
How Does a Traditional VPN Work?
A remote access VPN builds an encrypted tunnel from the user's device to a gateway at the edge of the corporate network. Once authenticated, the device usually receives an internal IP address and can reach many internal systems, limited only by firewall rules. NIST SP 800-46 covers securing this telework model. See how a VPN works for the basics.
How Do the Two Approaches Compare?
| Aspect | Traditional VPN | Zero Trust Exchange style access |
|---|---|---|
| What the user reaches | A network segment | Specific named applications |
| Trust after login | Often broad and persistent | Evaluated per request |
| Exposure of apps | VPN gateway listens on the internet | Apps reached through outbound connectors |
| Lateral movement risk | Higher if credentials are stolen | Lower, no network-level access |
| Traffic inspection | Depends on separate tools | Built into the cloud service |
| Main dependency | On-premises appliances | The vendor cloud service availability |
Why Are Organisations Moving Away From VPNs?
VPN appliances sit on the internet and hold privileged access, so attackers target them. Many VPN and remote access products appear in CISA's Known Exploited Vulnerabilities catalog. The NSA network pillar guidance recommends segmentation and limiting lateral movement, which app-level access supports. Cloud adoption also means much traffic no longer needs to pass through the data centre.
| Consideration | Question to ask |
|---|---|
| Legacy apps | Do any need full network access or unusual protocols? |
| Vendor dependency | What happens if the cloud service has an outage? |
| Privacy and TLS inspection | Which traffic must be excluded from decryption? |
| Data location | Where are logs stored, and does that meet DPDP and CERT-In log rules? |
How Should You Plan a Migration?
- Inventory applications and who needs each one.
- Strengthen identity first: phishing-resistant MFA and single sign-on.
- Add device posture checks.
- Move low-risk apps first, then retire VPN access group by group.
- Keep logs for 180 days in line with CERT-In directions.
Zscaler is one vendor in this market; compare several against the NIST and CISA models. To learn zero trust design hands-on, ask about network and cloud security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.